A critical client decision was ready to move. The business owner had approved it. Finance had completed its review. Compliance had assessed the risk, and the commercial terms were ready.
One final governance approval remained.
Three days passed.
Then five.
Then eight.
Nothing was fundamentally wrong with the decision. No new risk had appeared. No information was missing. The organisation had simply reached a point where too many important decisions were moving through too many approval points at the same time.
The business was still operating.
Governance was still functioning.
But governance had become a queue.
This is one of the less visible consequences of organisational growth. As organisations expand across business units, jurisdictions, service lines, and regulatory environments, additional controls are introduced to strengthen oversight. Each control may make sense individually, but collectively they can create layers of review that slow decisions, obscure ownership, and make it difficult for leadership to understand where critical work is actually waiting.
The result is not necessarily weak governance.
It can be too much governance without enough flow.
Approval controls exist for a reason.
They protect organisations from poorly considered decisions, financial exposure, regulatory breaches, inappropriate commitments, and uncontrolled operational activity. As businesses become more complex, additional approval requirements naturally emerge around these risks.
The problem begins when those requirements accumulate without the underlying process being redesigned.
A single decision may require review from a business manager, finance, compliance, legal, risk, regional leadership, and an executive committee. Every reviewer may have a legitimate role, yet the overall process becomes increasingly difficult to navigate.
The business may know that something is delayed without knowing why.
Management may know that an approval is outstanding without knowing where it is sitting.
The person responsible for moving the decision forward may have no visibility into what is happening elsewhere in the process.
That is where a governance control becomes a governance bottleneck.
The obvious cost of approval congestion is time.
The less obvious cost is everything that accumulates while the decision is waiting. A client proposal remains unresolved, a supplier cannot be appointed, a contractual commitment remains unsigned, or an operational change sits between departments because one final approval has not been completed.
Individually, each delay may appear manageable.
Across an organisation, they begin to create a pattern.
Teams start following up manually. Employees send reminder emails. Managers maintain private trackers. Decisions are escalated informally. People begin asking colleagues whether an approval has moved rather than checking a reliable governance process.
Eventually, the organisation creates a second process around the first process simply to understand what is happening.
That is usually a sign that governance has become difficult to operate.
Effective governance does not mean removing controls.
It means making controls proportionate, visible, accountable, and operationally efficient.
A high-value transaction may reasonably require several levels of review. A routine operational decision may not. A decision involving significant regulatory exposure may require specialist oversight, while a lower-risk activity may need only a standard approval.
When every decision follows the same path regardless of risk, governance can become unnecessarily expensive.
This is why mature governance environments need to distinguish between the existence of a control and the effectiveness of that control.
A process that prevents inappropriate decisions but routinely delays legitimate ones may still require redesign.
The objective is not fewer controls.
It is better-controlled decision flow.
The Saudi Central Bank (SAMA) requires financial institutions under its governance principles to establish explicit powers and responsibilities and to set clear limits for responsibility and accountability. Its principles also call for written policies defining powers delegated to executive management, including how those powers are implemented and the period of delegation.
This becomes particularly relevant as organisations scale. Governance cannot depend only on who is authorised to make a decision; the organisation also needs a controlled way to move that decision through the right governance points.
At the international level, the Basel Committee on Banking Supervision for International Settlements (BIS) places strong emphasis on transparent responsibilities, effective governance structures, and processes that support oversight and accountability. Its current 2026 operational risk guidance also highlights clear responsibility, reporting relationships, issue tracking, escalation, and effective resolution mechanisms.
The underlying principle is straightforward: governance should provide control without making accountability or decision-making unnecessarily difficult to operate.
Approval congestion rarely starts with one badly designed workflow.
It develops as organisations add requirements over time.
A finance review is introduced after a new risk emerges. Compliance adds another checkpoint following a regulatory change. Legal requires additional review for a new category of contract. Regional management introduces another layer to maintain local oversight.
Each addition appears reasonable.
The difficulty is that nobody may be responsible for looking at the complete decision journey.
One team sees its own checkpoint.
Another sees its own responsibility.
Leadership sees the outcome.
Very few people see the entire queue.
Consider a professional services organisation operating across several GCC markets.
A major client engagement requires commercial approval, financial validation, compliance review, legal confirmation, and regional leadership sign-off before the contract can be finalised. None of these controls is unnecessary. Each protects an important part of the organisation.
The difficulty emerges when several large engagements enter the approval process simultaneously.
Requests begin accumulating between departments. Some approvals are completed within hours, while others remain untouched for several days. Teams start sending follow-up emails to individual approvers, while managers create separate spreadsheets to track pending decisions.
Leadership can see that approvals are slowing down.
What it cannot immediately see is where the bottleneck is forming.
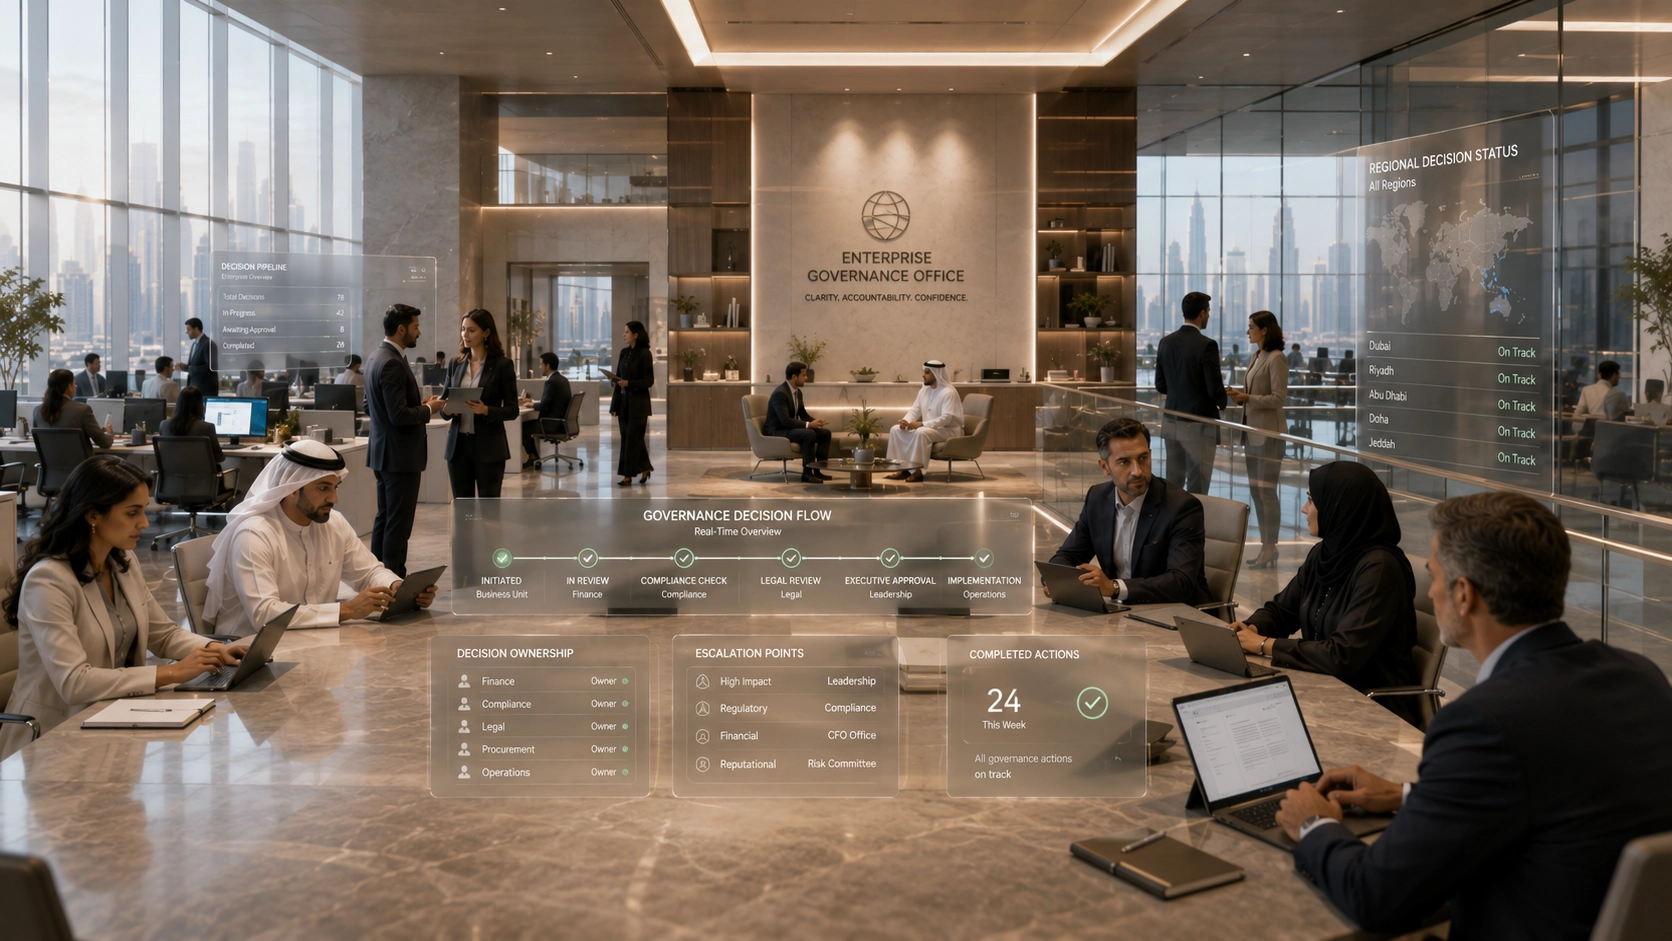
The organisation eventually redesigns its approval environment around structured workflow management. Approval responsibilities become explicit, requests move automatically to the appropriate reviewer, outstanding actions generate alerts, and management gains visibility into where decisions are waiting.
The organisation does not remove its governance controls.
It makes those controls operationally visible.
A governance review does not necessarily ask why one approval took six days.
The more important question is what the delay reveals about the control environment.
Reviewers may want to understand who was responsible for the approval, whether the request reached the correct authority, how long it remained pending, whether escalation mechanisms existed, and whether management could identify recurring delays.
They may also examine whether approval responsibilities were clearly defined and whether decision-making authority was structured consistently across the organisation.
This matters particularly where governance processes span multiple departments or jurisdictions.
A delayed approval may be an isolated event.
A recurring approval queue can reveal a much broader weakness in how governance has been designed and managed.
The most effective approval environments do something surprisingly simple.
They make waiting visible.
Instead of relying on email reminders or individual follow-ups, decision-makers can see which requests are pending, who owns the next action, how long the request has been waiting, and whether escalation is required.
That visibility changes behaviour.
Approvers can prioritise outstanding decisions. Managers can identify recurring bottlenecks. Compliance teams can monitor governance-sensitive activities. Leadership can distinguish between genuine risk-based delays and process inefficiencies.
More importantly, the organisation begins to understand its own governance processes.
It can identify where approvals consistently accumulate.
It can measure how long decisions take.
It can determine whether certain controls are creating unnecessary friction.
And it can improve the process without weakening oversight.
There is an important distinction between governance that slows decisions and governance that makes decisions safer.
The first creates friction.
The second creates confidence.
Organisations need approval structures that allow the right people to intervene at the right moment, with the right information, while keeping the entire decision journey visible.
That requires more than an approval matrix sitting inside a policy document.
It requires an operational system capable of moving decisions through governance processes consistently.
This is where Moebius Workflow Automation becomes valuable.
Through its integrated platform, Moebius brings business processes, accountability, auditability, and governance into a connected operating environment. Its platform is designed to support integrated business processes while maintaining audit and accountability across organisational activities.
Instead of managing approval requests through disconnected emails, spreadsheets, and manual follow-ups, structured workflows can route activities to the appropriate people, maintain visibility over outstanding actions, and preserve an auditable history of what happened throughout the process.
This allows workflow automation in the UAE and broader governance workflow GCC requirements to be approached as an operational governance capability rather than simply an automation exercise.
The objective is not to automate governance for the sake of automation.
It is to make governance visible, accountable, and capable of moving at the speed the organisation requires.
As organisations grow, governance will inevitably become more complex.
More jurisdictions create more requirements. More business units create more decision-makers. More regulatory expectations create additional controls. More operational activity creates more decisions that require oversight.
The answer is not to remove that complexity.
It is to manage it intelligently.
Organisations need to know which decisions require approval, who owns each stage, where requests are waiting, when escalation is necessary, and whether governance processes are supporting or obstructing operational execution.
That is the difference between having approval controls and having governed decision flow.
The organisations that manage this well do not compromise between governance and agility.
They build governance into the way decisions move.
The question leadership should be asking is no longer:
“How many approvals does this process have?”
It is:
“Can we see where every critical decision is, who owns the next action, and whether our governance process is helping the business move forward?”
Provide us with a bit of information about your business needs and we will be in touch to arrange a no commitment demonstration.


"*" indicates required fields