Operational resilience is becoming a more demanding governance discipline across the GCC. For regulated organisations, maintaining a Business Continuity Plan is no longer enough if the organisation cannot demonstrate that its critical operations, dependencies, responsibilities, recovery arrangements, and testing remain current.
The question is shifting from whether a continuity plan exists to whether the organisation can prove that its resilience arrangements are capable of working when normal operations are disrupted. That requires evidence generated through governance, testing, review, monitoring, and corrective action rather than documentation alone.
In the UAE, this direction is reflected in the CBUAE Operational Risk Management Regulation C 1/2026, which places operational resilience within the broader operational risk framework for licensed financial institutions.
Every organisation has activities that matter more than others during a disruption. Customer services, payment processing, regulatory reporting, transaction processing, technology platforms, and other critical operations may have different tolerances for interruption.
Understanding these priorities is the foundation of resilience. An organisation needs to know which operations are critical, what people and technologies support them, which processes and data they depend on, and which third parties or external services could affect their ability to continue.
Without this understanding, continuity planning can become a collection of recovery procedures without a clear connection to the business activities that actually need protection.
Consider a financial institution that reviews its Business Continuity Plan every year. The document identifies key systems, assigns responsibilities, defines recovery procedures, and includes contact details for critical teams.
During that same period, the organisation changes a technology provider, restructures a business function, introduces a new digital service, and outsources part of an operational process.
The organisation may still have a formally approved continuity plan. But some of the assumptions behind that plan may no longer reflect how the business actually operates.
This creates a subtle resilience risk: the organisation believes it is prepared because its documentation is complete, while its operating environment has moved on.
The CBUAE’s 2026 framework treats operational resilience as an ongoing capability rather than a static planning exercise. Its requirements address the ability to respond to, adapt to, recover from, and learn from disruptive events while minimising the impact on critical operations.
That approach places greater emphasis on understanding vulnerabilities and dependencies before disruption occurs. It also connects resilience with the wider operational risk framework, meaning changes in the business can have direct implications for how resilience arrangements should be maintained.
For organisations operating in regulated environments, this creates a practical governance requirement: resilience needs to evolve as the organisation evolves.
A continuity plan tells an organisation what it intends to do.
A test provides evidence of what happens when those arrangements are put under pressure.
Testing can reveal whether recovery objectives are realistic, whether employees understand their responsibilities, whether escalation channels work, whether critical suppliers respond as expected, and whether technology recovery arrangements function as intended.
A successful exercise should therefore not simply produce a positive result. It should produce information that management can use to strengthen the organisation’s resilience.
A resilience exercise may reveal that a recovery process took longer than expected or that a critical dependency was not available when required. It may expose unclear ownership, outdated contact information, insufficient capacity, or an unexpected dependency between two business functions.
These findings are valuable because they reveal weaknesses before a real disruption does.
The governance challenge begins after the exercise: findings need to be recorded, responsibilities need to be assigned, corrective actions need to be tracked, and management needs visibility over whether those actions have actually been resolved.
That is where resilience evidence becomes more meaningful than a simple statement that testing has been completed.
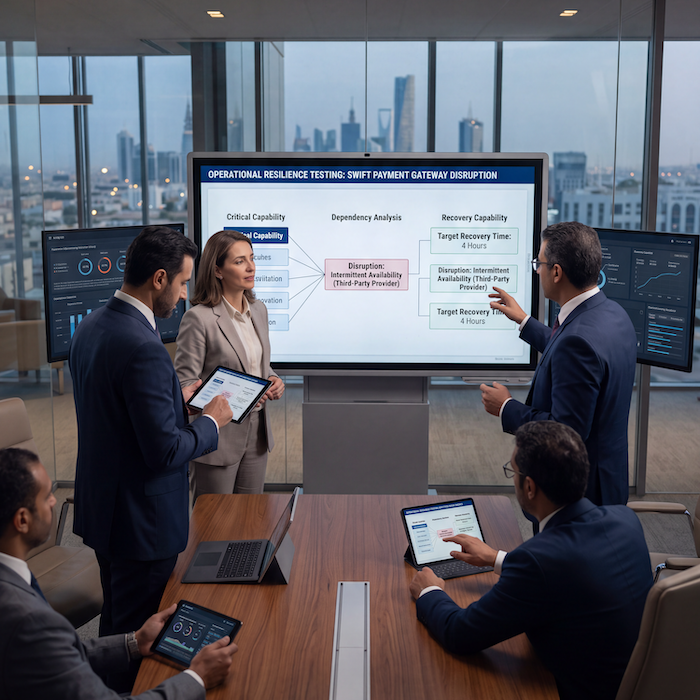
Modern organisations rarely operate entirely within their own four walls. Cloud providers, payment infrastructure, technology vendors, specialist service providers, and other third parties can become essential to critical operations.
That means an organisation’s resilience cannot be assessed solely through its internal continuity arrangements.
If a critical operation depends on an external provider, the organisation needs appropriate visibility into that dependency and the resilience arrangements surrounding it. Otherwise, an apparently robust internal recovery plan may depend on an external capability that has never been adequately assessed or tested.
This is particularly important for regulated financial institutions where operational disruption can quickly affect customers, transactions, reporting, and regulatory obligations.
Business continuity arrangements can become outdated without any obvious warning.
A new product can introduce a new operational dependency. A technology migration can change recovery requirements. An outsourcing decision can transfer part of a critical process to a third party. An organisational restructure can change who owns a resilience activity.
Each of these changes can alter the assumptions behind an existing resilience framework.
That is why resilience governance needs to remain connected to change management, operational risk, technology, third-party management, and business ownership rather than operating as an isolated annual exercise.
A mature resilience framework should allow management to answer straightforward questions without having to reconstruct the information manually.
Which operations are critical? What do they depend on? Who owns their resilience? When were the relevant arrangements last reviewed? When were they tested? What weaknesses were identified? Who owns the resulting actions? Have those actions been completed?
The strength of the framework is not determined by how many documents an organisation maintains. It is determined by how confidently management can connect those documents, decisions, responsibilities, tests, findings, and corrective actions into one current picture of resilience.
This is an important distinction for organisations operating under increasingly demanding regulatory expectations.
A continuity document describes an intended response. Resilience governance creates an ongoing mechanism for ensuring that the response remains relevant, tested, owned, and capable of supporting critical operations.
The difference becomes especially important when an organisation has multiple entities, complex technology environments, external providers, or operations spread across different locations.
The more complicated the operating model becomes, the harder it is to maintain resilience through documents alone.
This is where Moebius can support the governance environment around operational resilience.
Möbius brings document management, workflows, reporting, compliance, corporate management, and other business functions together within an integrated platform. Its document management capabilities support centralised storage, retrieval, version control, access management, workflows, approvals, and recoverability, helping organisations maintain better control over the information that supports ongoing governance.
The value is not simply having another place to store a Business Continuity Plan. It is creating a connected environment in which relevant documents, responsibilities, approvals, actions, reviews, and management information can be managed as part of the wider operational framework.
Through Moebius Document Management, organisations can centralise critical documents, manage versions, configure approval workflows, set reminders, control access, and retrieve information efficiently when it is required.
That becomes particularly useful when resilience activities generate evidence across multiple teams. Instead of allowing test results, actions, supporting documents, and approvals to exist in disconnected locations, organisations can bring those activities into a more structured governance environment.
The strongest resilience evidence is created before an organisation experiences a major disruption.
It comes from current critical-operation mapping, tested recovery arrangements, reviewed dependencies, defined responsibilities, documented findings, completed corrective actions, and management oversight.
When these elements are maintained continuously, an organisation is better positioned not only to respond to disruption but also to demonstrate why its resilience arrangements remain credible.
That is a fundamentally different position from discovering during an incident that the organisation’s plan was never fully aligned with the business it was supposed to protect.
GCC organizations should not assume that regulatory alignment means every jurisdiction will operate identically.
Local regulators have their own supervisory priorities, licensing frameworks, reporting expectations, and implementation requirements. The objective should therefore be to create a common governance structure while preserving the flexibility required for local compliance.
That approach gives central leadership a consistent view without forcing local entities into an inappropriate one-size-fits-all model.
It also makes regulatory differences visible rather than allowing them to emerge informally through disconnected local decisions.
The question is no longer simply:
A stronger question is:
That is the difference between having a continuity plan and having evidence of operational resilience.
For organisations operating in the GCC, resilience will increasingly depend on the ability to connect critical operations with the people, processes, technology, third parties, governance activities, and evidence required to keep them functioning.
Provide us with a bit of information about your business needs and we will be in touch to arrange a no commitment demonstration.


"*" indicates required fields